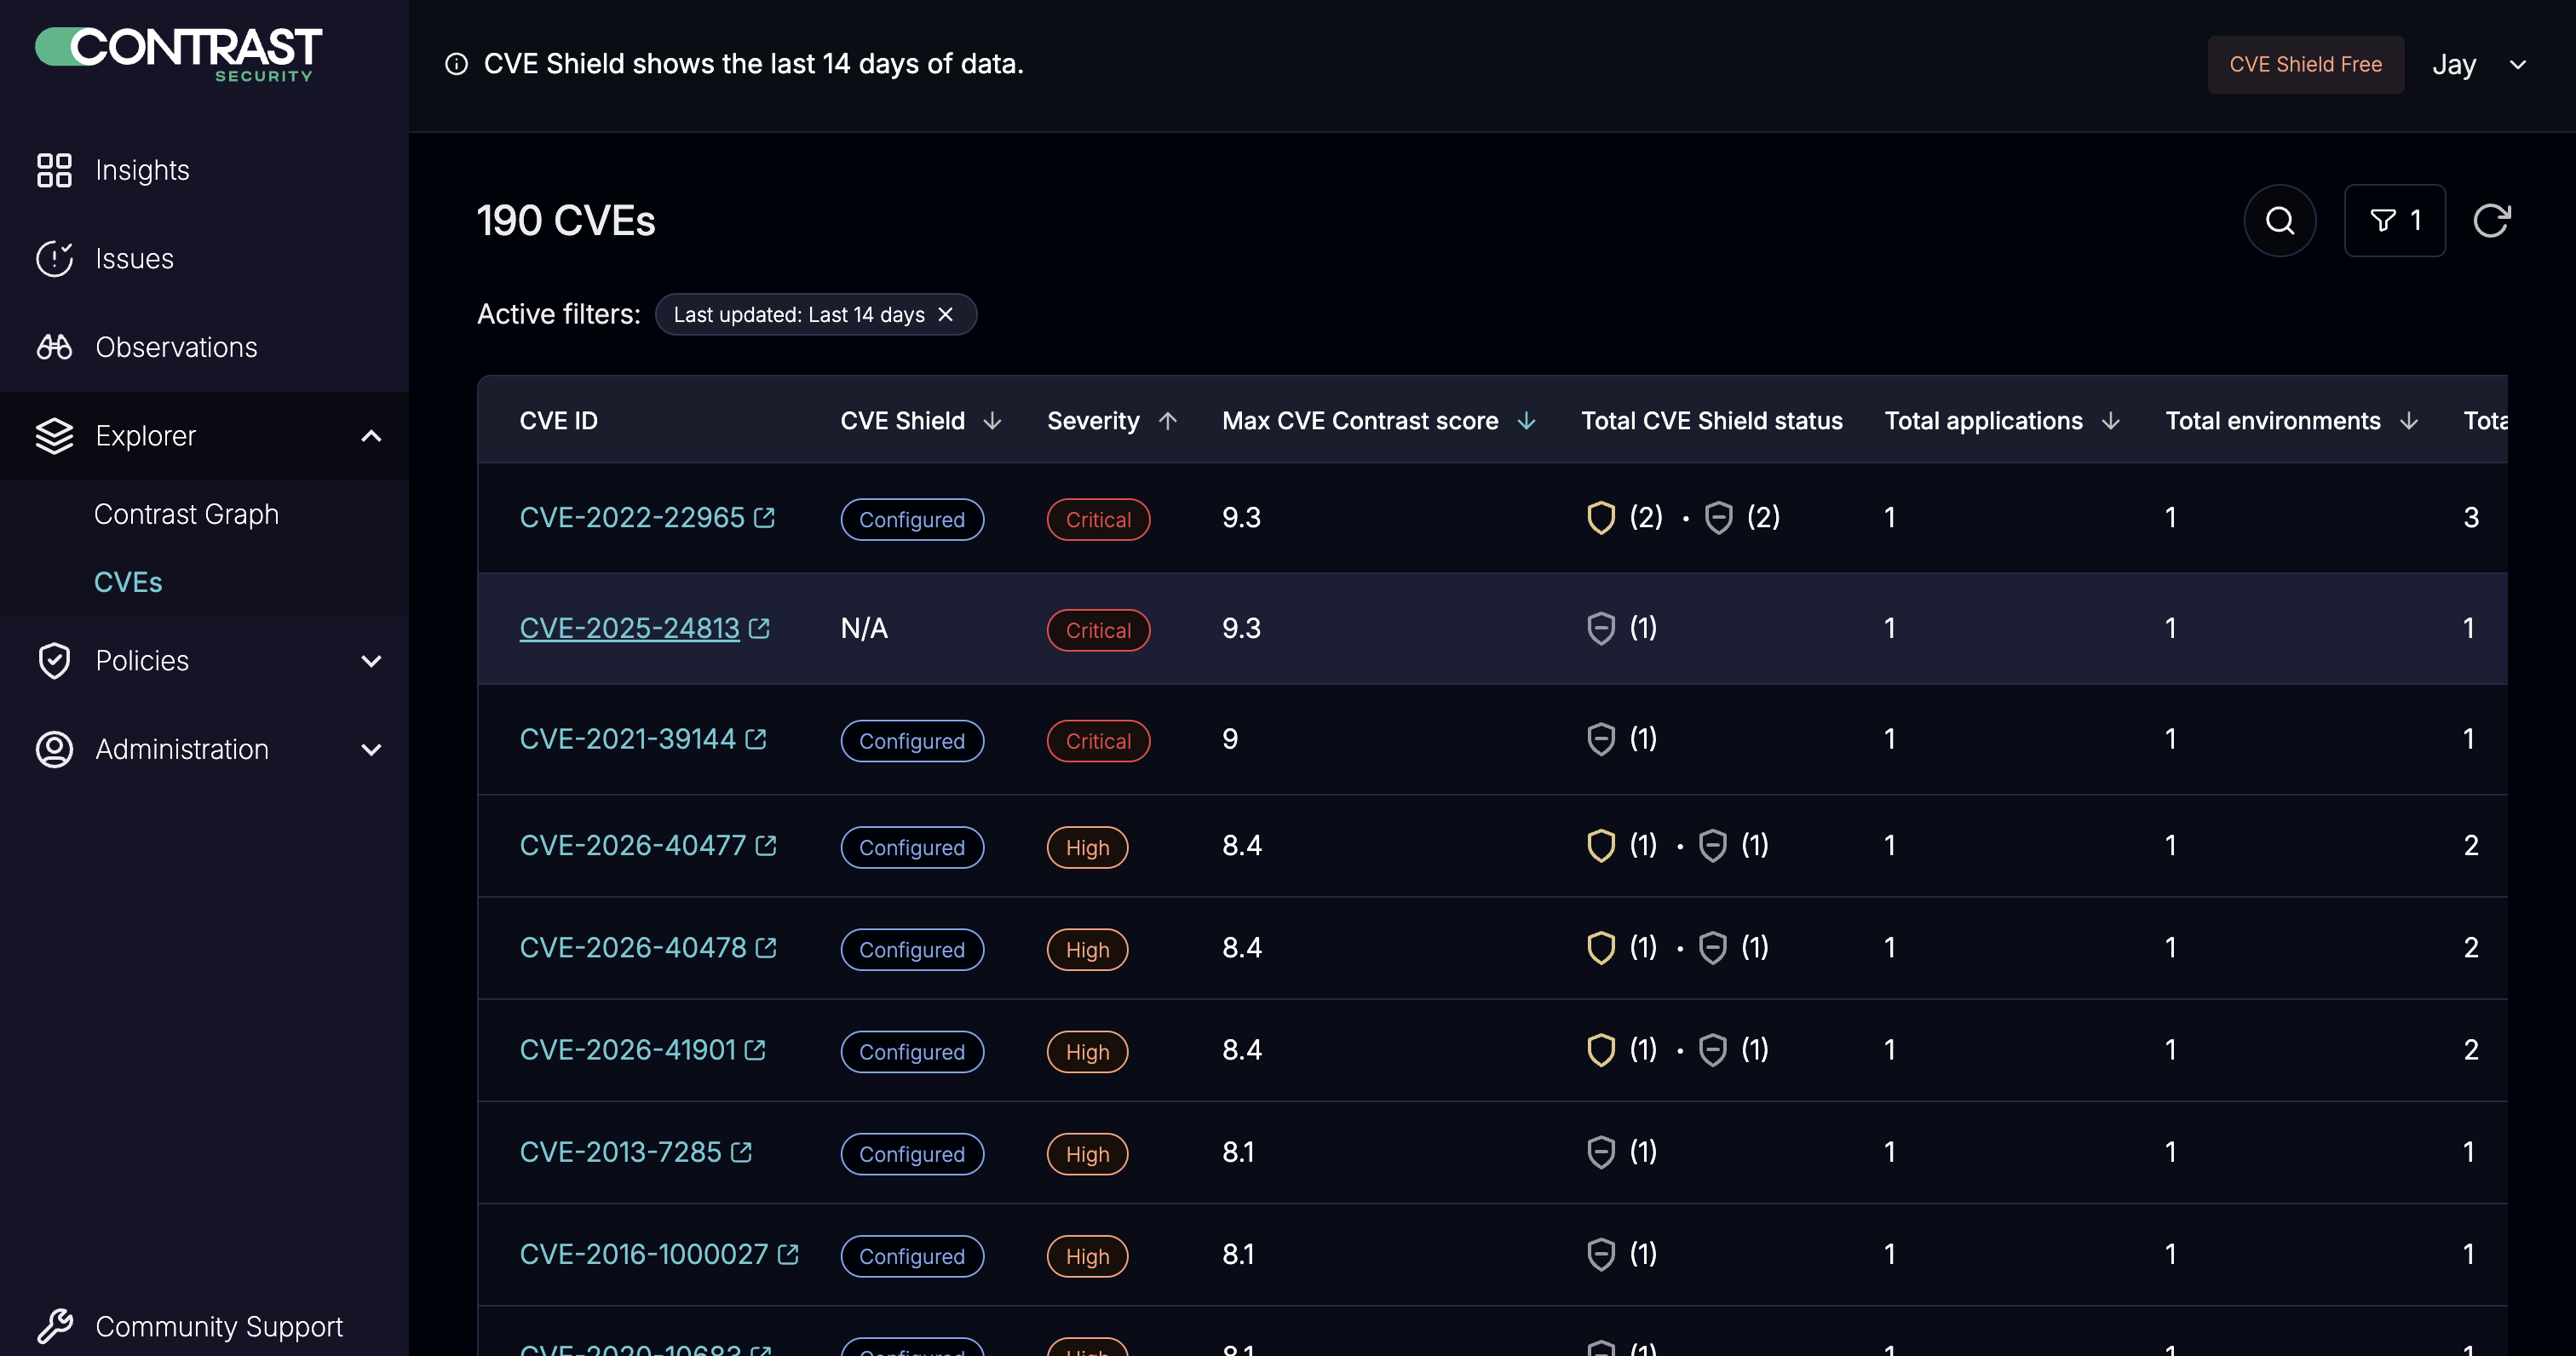
CVE Shield Free tier - confirming whether Assess vulnerability data (orgtraces/filter) is included Answered

We're currently on the CVE Shield Free tier and are trying to confirm exactly what vulnerability data this tier includes, since we're not seeing the results we expected from one of your API endpoints. We'd appreciate a direct confirmation so we can plan next steps correctly.
Agent: Contrast Flex Agent, Java, version 6.33.1
What we've done so far:
1. Installed the Contrast Flex Agent via the standard install script and confirmed it attaches successfully to our Java application (JAVA_TOOL_OPTIONS auto-injection confirmed).
2. Enabled Assess, Protect, and Observe explicitly in /etc/contrast/contrast_security.yaml. The agent's own startup log confirms:
Effective instructions: Assess=true, Protect=true, Observe=true, Shield=true
3. Deployed a small test application (an intentionally vulnerable Spring Boot app with a SQL injection endpoint) and sent a mix of valid and SQL-injection-payload requests directly to it, confirming (via server-side logs) that the requests were received and processed by the instrumented JVM.
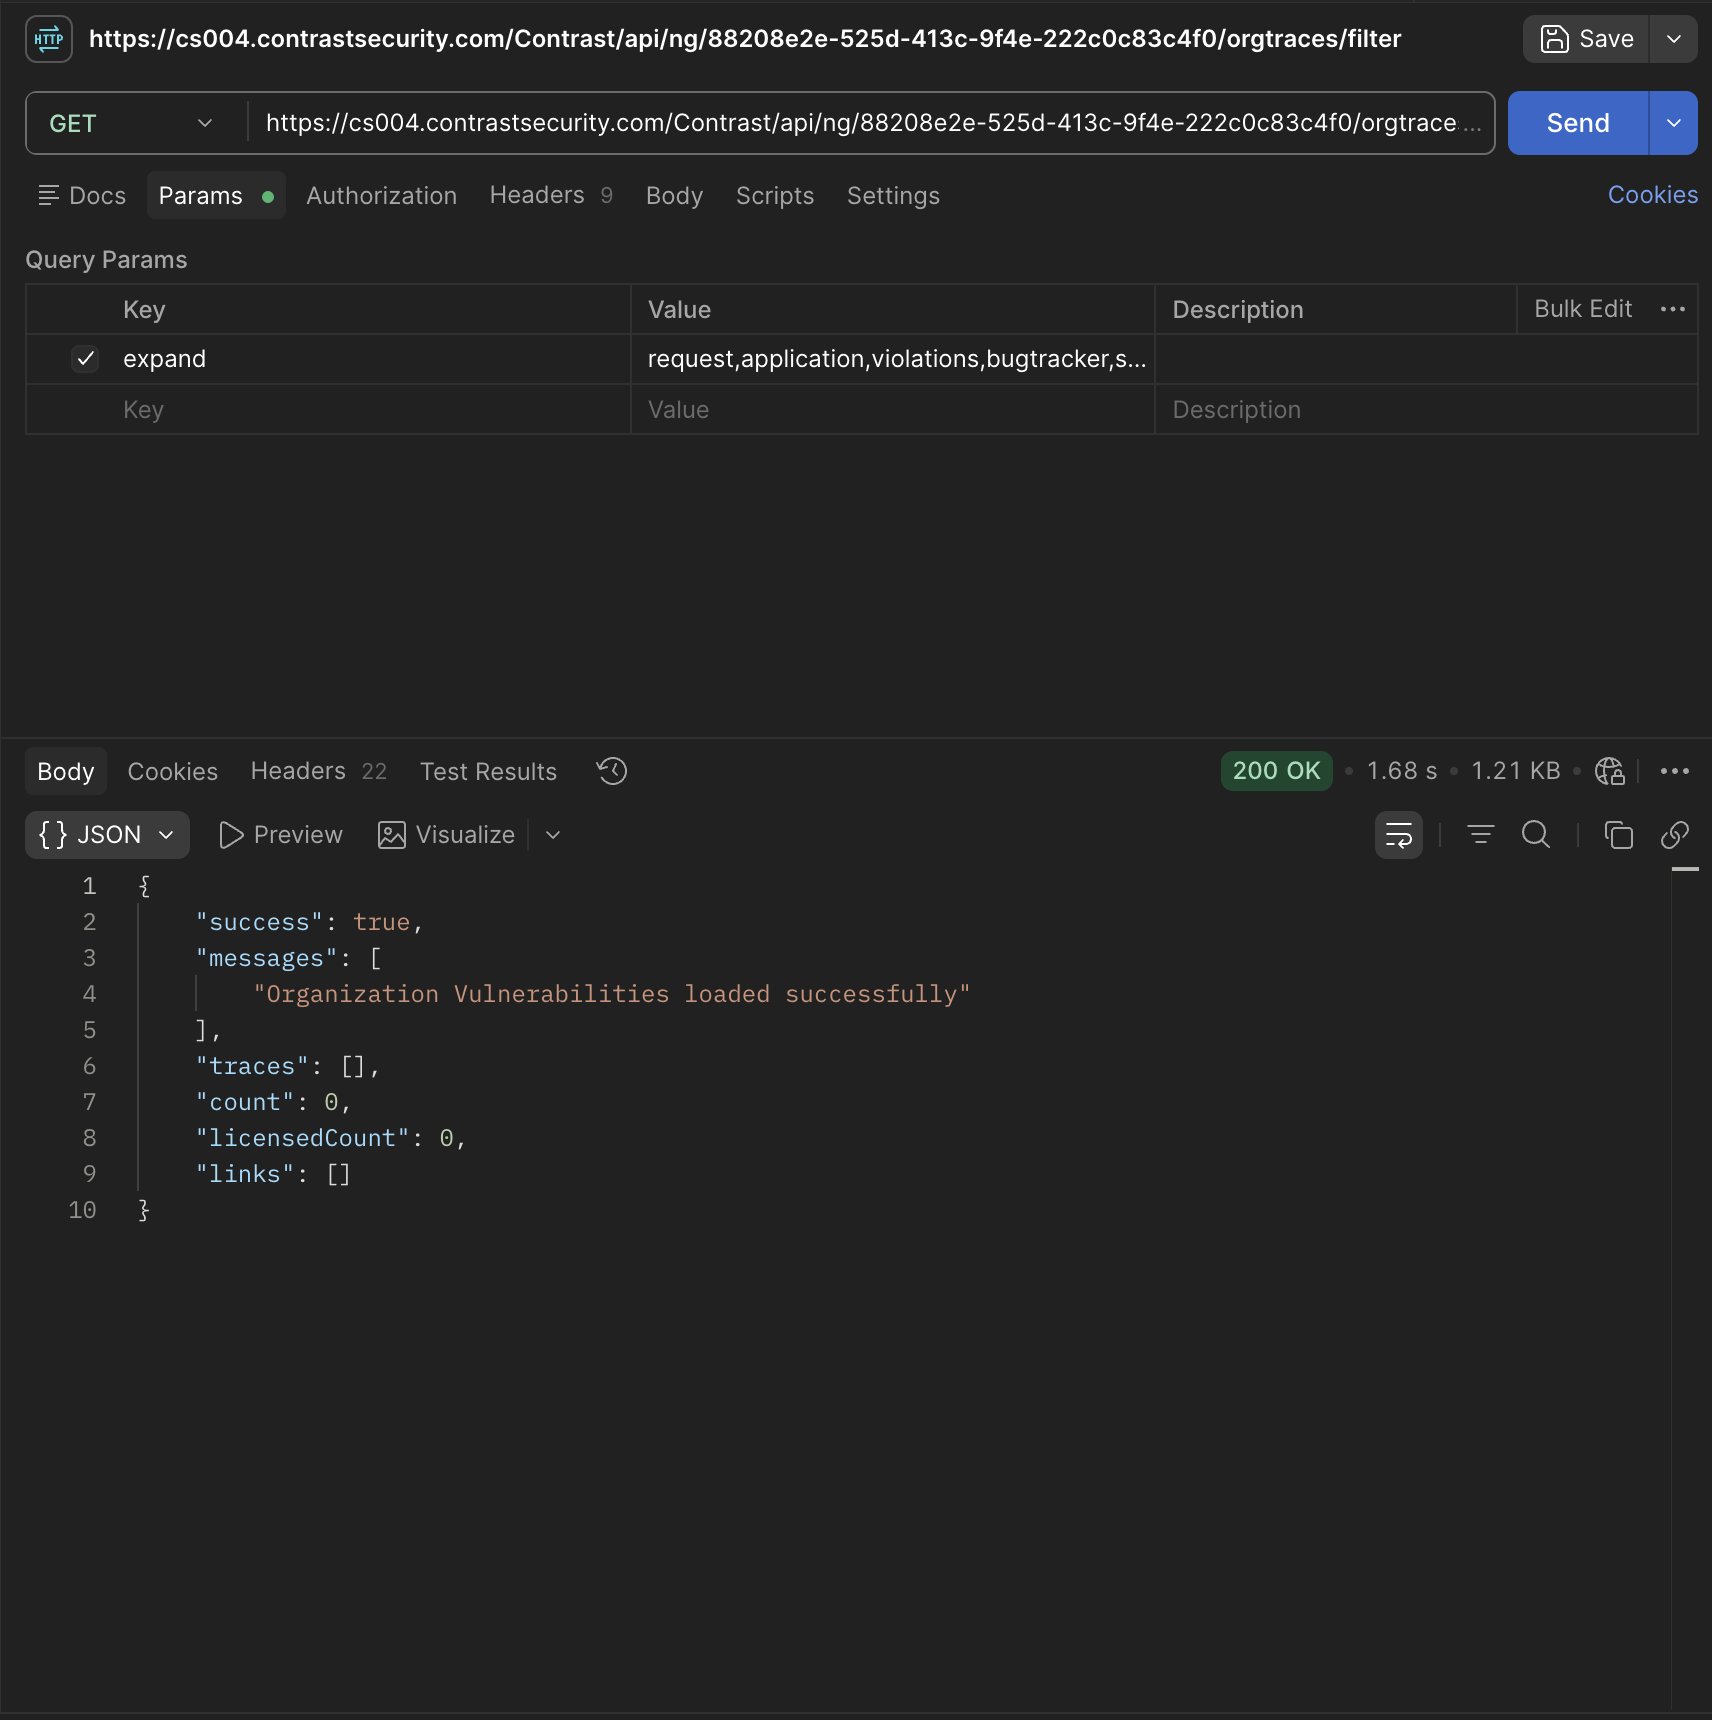
4. Queried the Organization Vulnerabilities endpoint directly:
GET https://{our-teamserver-url}/Contrast/api/ng/{orgUuid}/orgtraces/filter
This consistently returns:
{ "success": true, "count": 0, ... }
even after generating real SQL injection traffic against the instrumented application.
What we're trying to confirm:
Based on your own documentation (specifically "Try Contrast for free" - https://docs.contrastsecurity.com/en/try-contrast-for-free.html - under "What CVE Shield is not"), it appears CVE Shield Free is scoped to monitoring known CVEs (Incidents, Issues, Observations) rather than the general Vulnerability/Trace data model that Assess produces and that the orgtraces/filter endpoint returns. We also reviewed https://docs.contrastsecurity.com/en/assess.html, which describes Assess as a distinct, separately-enabled capability.
Could anyone please confirm directly:
1. Does the CVE Shield Free tier include Assess-generated vulnerability findings (e.g., SQL injection, custom-code data-flow vulnerabilities) via the orgtraces/filter endpoint, or is that gated behind a separate Assess/ADR license?
2. If Assess/ADR is required, is a trial or add-on available to evaluate this capability?
3. Are we missing anything for the Vulnerability/Traces generation?
Comments
1 comment
Hi Jay,
We appreciate your interest and detailed questions. These questions will help other CVE Shield users as well as contribute to improvements to our FAQs. To address your questions directly:
1. Does the CVE Shield Free tier include Assess-generated vulnerability findings (e.g., SQL injection, custom-code data-flow vulnerabilities) via the orgtraces/filter endpoint, or is that gated behind a separate Assess/ADR license?
No. CVE Shield's Free tier includes Runtime CVE-related data only.
2. If Assess/ADR is required, is a trial or add-on available to evaluate this capability?
To evaluate other products like Assess and ADR, please reach out to our sales team at +1 888-371-1333.
3. Are we missing anything for the Vulnerability/Traces generation?
The
orgtracesendpoint will only return vulnerabilities from Code analyses such as IAST. To look for CVE details via the API, please check thelibrariesendpoint, e.g.https://{our-teamserver-url}/Contrast/api/ng/{orgUuid}/libraries/filter?quickFilter=VULNERABLE…. This endpoint is documented here: https://github.com/Contrast-Security-OSS/contrast-teamserver-api-docs/blob/main/saas-restapi-v3/library/Libraries/README.mdKind Regards,
Jon
Please sign in to leave a comment.